 Jason Finance
Ledger Theft Incident: Users Who Bought from Reseller CryptoBilis Lose Nearly US$90 Million. The Known Facts and the Checks to Run When You Set Up a Cold Wallet
Ledger theft: Ledger is investigating losses among users who bought from reseller CryptoBilis, put at over US$86 million. Known facts, official advice, checks.
On this page
- 1.What we know so far
- 1.1Ledger’s official advice
- 2.Claims that have not been confirmed
- 2.1How to verify crypto news
- 3.Why I am paying close attention: I just bought a new Ledger
- 4.How to confirm a new cold wallet is brand new and untampered
- 4.1When you buy
- 4.2During setup: check each item
- 4.3In everyday use
- 5.If you bought from CryptoBilis
- FAQ
On the evening of 9 October 2026, Ledger said it was investigating the theft of assets from a group of users in South East Asia, all of whom had bought their devices from a reseller called CryptoBilis. On-chain analysts estimate the losses at more than US$86 million, and Tether has frozen USDT on some of the related addresses. I bought a new cold wallet from Ledger only a few days ago, so I have been following this closely, and I noticed that many Chinese-language news flashes tell only half the story.
The short version: what we know so far is that devices bought from one particular reseller had a problem. The cause is still under investigation, and there is no evidence that every Ledger is unsafe. If you bought from CryptoBilis in the last 90 days, follow Ledger’s advice. If not, buy any cold wallet directly from the official website or an authorized reseller, and during setup make sure the recovery phrase is generated by the device itself, the device passes the Genuine Check, and the first address has no transaction history.
This article summarizes public information available as of the evening of 9 October 2026 (Taiwan time, UTC+8). The incident is still under investigation, and the figures and cause may change; I will update this article as the investigation progresses. This article is not investment or security advice.
What we know so far
| Time (Taiwan time, UTC+8) | Source | What was reported |
|---|---|---|
| 9 October, 21:32 | Ledger Support (X) | Investigating “reports of loss of funds from users in South East Asia” who bought products from the reseller CryptoBilis; has “asked CryptoBilis to pause all sales and shipments of Ledger devices” |
| 9 October | On-chain analyst Specter (X) | Traced suspicious addresses on Bitcoin, Ethereum and Tron; estimates hundreds of wallets drained and losses above US$86 million |
| 9 October, 23:19 | MistTrack (X) | Tether has frozen a large amount of USDT on some of the related addresses; losses are close to US$90 million |
| 9 October | Lookonchain (as reported by Odaily) | One user bought a device three weeks earlier, deposited 7 million USDT and had all of it stolen, possibly the largest single loss in this incident |
CoinDesk’s report specifically notes that neither the loss figure nor the link between these thefts has been independently verified, and Ledger’s statement does not confirm the amount lost or the cause (CoinDesk).
Ledger’s official advice
Ledger’s statement gives two recommendations, aimed at users who bought from CryptoBilis in the last 90 days:
- If you have not set up your device yet, do not start the setup.
- If you already have, consider moving your assets to another new Ledger with a newly generated recovery phrase.
For any questions, contact Ledger only through Ledger’s official support.
Claims that have not been confirmed
Each of the Chinese-language news flashes I saw covered only part of the story, and some added speculation:
- “Ledger was hacked”: Ledger’s statement only says it is investigating losses among users who bought from a particular reseller. It does not say Ledger itself was hacked.
- “Weak random numbers let attackers guess the recovery phrases”: this is speculation. Ledger has not confirmed any technical cause.
- “A supply chain attack”: Changpeng Zhao said that, based on current information, it looks like a supply chain attack through a single reseller, in which a small number of users may have received counterfeit or tampered devices (The Cryptonomist). This is the explanation most widely cited right now, but it is not an investigation finding either.
So the more accurate statement is: devices bought from one reseller appear to have had a problem, and the cause is under investigation. When you see claims that “no Ledger is safe” or that “a specific vulnerability has been confirmed,” go back and check what Ledger’s official account has actually said.
How to verify crypto news
Here is what I did this time:
- Find the official account of the company involved: in this case, @Ledger_Support. What the company says, and what it does not say, matters more than a news flash headline.
- Find where the numbers come from: the “US$90 million” figure comes from on-chain analysts’ tracking. Ledger did not publish it.
- Watch for the words “not yet confirmed”: reliable outlets spell out what is still unverified. News flashes often leave it out.
- Scams that follow the incident: big events are often followed by fake support agents, fake compensation offers and fake “security check” websites that ask for your recovery phrase. The real Ledger will never ask you to enter your recovery phrase on a computer, phone or website (Ledger guide).
Why I am paying close attention: I just bought a new Ledger
A few days ago I bought a new cold wallet from Ledger and I am waiting for it to arrive, which is why I have been following this so closely. While tracking the story, I realized how much crypto news needs checking: many of the Traditional and Simplified Chinese reports I read told only half of what happened.
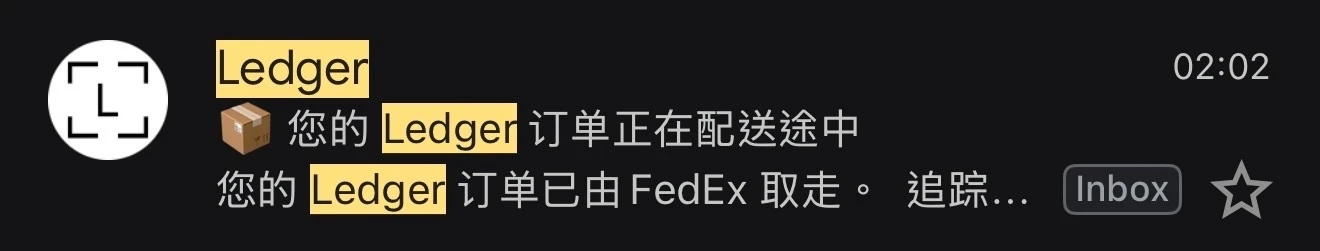 The Ledger shipping notification I received (Chinese interface), screenshot from October 2026
This time the problem was in a reseller channel. Ledger itself explains that its Genuine Check can confirm the secure element inside the device is genuine, but it cannot detect a device where the secure element is intact and other hardware has been added, and it cannot verify whose hands the device passed through in transit (Ledger guide). So who you buy from is part of your security.
How to confirm a new cold wallet is brand new and untampered
A cold wallet’s security rests on one thing: only you know the recovery phrase. The recovery phrase is 24 English words that can restore all of your private keys, and whoever has it can move your assets. The typical supply chain attack generates a recovery phrase before the device reaches you, keeps a copy, and moves your assets once you deposit them (Ledger calls this “pre-seeded,” meaning the recovery phrase was planted in advance).
When you buy
- Buy from the Ledger website, or choose from Ledger’s published list of official authorized resellers. Buying directly from the official website removes one middleman.
- Do not buy second-hand, auctioned or unknown-origin devices, however cheap they are.
- If the packaging looks opened or altered, do not use the device. Contact Ledger support directly.
During setup: check each item
- The recovery sheet must be blank: Ledger’s recovery sheets are always blank, and devices never come with a preset recovery phrase or PIN. If the sheet already has words printed or written on it, do not use it, and contact Ledger support (Ledger guide).
- Choose to set it up as a new device, and let the device generate 24 words on its own screen. Do not choose to restore from a recovery phrase and enter words someone else gave you.
- Complete the Genuine Check: download Ledger Wallet only from the Ledger website or an official app store. During setup it sends a verification request to the device to confirm the secure element is genuine (Ledger guide). If the device fails, do not use it.
- Confirm that the first receiving address is brand new: generate a receiving address in Ledger Wallet, go by the address shown on the device screen, and look it up in a block explorer for that chain (for example, Etherscan for Ethereum, Tronscan for Tron, mempool.space for Bitcoin). A brand new address should have no transactions at all. Any history or balance means the recovery phrase has been used before, so do not deposit any assets.
- Use Recovery Check to confirm you wrote the words down correctly: Ledger’s Recovery Check confirms that the 24 words you copied are correct without exposing the recovery phrase.
- Test with a small amount first: deposit a small sum, then try sending a small sum out. Once both directions work, move larger amounts.
Item 4 has a limit: if an attacker prepared a recovery phrase that has never been used, its addresses will have no transaction history either. This check only catches a recovery phrase that has been used. It cannot prove on its own that the device is fine, so do it together with items 1 to 3.
In everyday use
- Write the recovery phrase only on paper or a metal plate. Do not photograph it, store it in the cloud or send it to anyone.
- Any website, app or support agent that asks for your recovery phrase is a scam.
- Spread large holdings out: do not keep all your assets under a single recovery phrase. In this incident, one user deposited 7 million USDT three weeks after buying the device and lost all of it.
If you bought from CryptoBilis
Follow Ledger’s advice:
- Not set up yet: do not set it up. Contact Ledger’s official support first.
- Already set up: consider moving your assets to another new Ledger bought from the official website or an authorized reseller, with a newly generated recovery phrase.
- Assets already moved out: keep the transaction records and contact Ledger’s official support. Security Alliance has also said that people whose assets were sent to the related addresses can contact it through the SEAL 911 Telegram bot (The Cryptonomist).
- Beware of fake helpers: anyone who claims they can recover your assets and asks for an upfront fee or your recovery phrase is almost always a scammer.
For the difference between a cold wallet and an exchange, and when to move assets off an exchange into your own wallet, see “What to do when you see warning signs” in How to check proof of reserves. More articles are on the crypto topic page.
FAQ
Does the Ledger theft mean Ledger's cold wallets have been cracked?
As of 9 October 2026, this has not been confirmed. Ledger's statement only says it is investigating losses among users who bought devices from CryptoBilis, a reseller in South East Asia, and gives no cause. The explanation most people are discussing is a supply chain problem, meaning the devices were tampered with before they reached users, but that is not an investigation finding either.
My Ledger was not bought from CryptoBilis. Do I need to do anything?
Ledger's recommendations only cover users who bought from CryptoBilis in the last 90 days. If you bought elsewhere, run the usual checks: the recovery phrase was generated by the device itself, the device passed the Genuine Check, and the first receiving address has no transaction history.
What should I do with a Ledger bought from CryptoBilis?
Ledger recommends that if you have not set it up yet, do not set it up. If you already have, consider moving your assets to another new Ledger with a newly generated recovery phrase. For any questions, contact Ledger only through its official support.
How do I confirm that a new cold wallet's address is brand new?
Confirm the first receiving address on the device screen and look it up in a block explorer for that chain. A brand new address should have no transactions at all. Any history or balance means the recovery phrase has been used before, so do not deposit anything. This check only catches a recovery phrase that has been used. It cannot prove the device is fine, so combine it with the other checks.
Where is it safest to buy a cold wallet?
Ledger recommends buying from the Ledger website or an official authorized reseller, and completing the Genuine Check during setup. In this incident, the problem was in a reseller channel, so buying directly from the official website removes one middleman. Do not buy second-hand devices or devices of unknown origin.
Jason
Account Manager in Google Large Customer Sales and Columbia MBA admit, sharing the money tools and experience he actually uses.
Comments
Sign in with Google to comment. Your comment will not show your Google profile picture or name; it appears under a randomly generated nickname to protect your privacy.
By signing in you agree to this site's privacy policy.